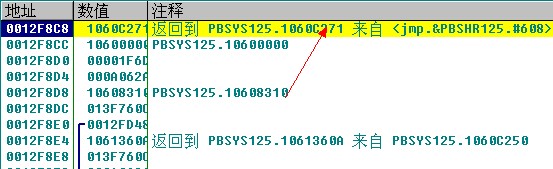
7. 重复 5-6 步骤一次 我们来到了这里 直接 看下面汇编代码 不要看着眼花 其实很简单
C# code?
123456789101112
13141516171
81920212223242526272829303
13233343536
37383940414243444546474849505
15253545556
5758596061626364656667686970717273747576777879808
18283848586
878889909192939495969798991001011021031041051061071081091101111121
13114115116
1171
18119120121
122123124125126127128129
13013113213
3
13413513613
7138 1061349F CC int3106134A0 /$ 55 push ebp ; 邪恶的入口 重点都在这里106134A1 |. 8BEC mov ebp,esp106134A3 |. 81EC 4C040000 sub esp,44C106134A9 |. 53 push ebx106134AA |. 33DB xor ebx,ebx106134AC |. 56 push esi106134AD |. 57 push edi106134AE |. 68 027F0000 push 7F02 ; /RsrcName = IDC_WAIT106134B3 |. 53 push ebx ; |hInst => NULL106134B4 |. 895D D0 mov dword ptr ss:[ebp-30],ebx ; |106134B7 |. 895D D8 mov dword ptr ss:[ebp-28],ebx ; |106134BA |. 895D E8 mov dword ptr ss:[ebp-18],ebx ; |106134BD |. 895D F4 mov dword ptr ss:[ebp-C],ebx ; |106134C0 |. 895D CC mov dword ptr ss:[ebp-34],ebx ; |106134C3 |. 895D F8 mov dword ptr ss:[ebp-8],ebx ; |106134C6 |. 895D E0 mov dword ptr ss:[ebp-20],ebx ; |106134C9 |. 895D D4 mov dword ptr ss:[ebp-2C],ebx ; |106134CC |. FF15 ECBA6810 call dword ptr ds:[<&USER32.LoadCursorW>] ; \LoadCursorW106134D2 |. 50 push eax ; /hCursor106134D3 |. FF15 E8BA6810 call dword ptr ds:[<&USER32.SetCursor>] ; \SetCursor106134D9 |. 8B75 08 mov esi,dword ptr ss:[ebp+8]106134DC |. 8945 C4 mov dword ptr ss:[ebp-3C],eax106134DF |. 8D45 D4 lea eax,dword ptr ss:[ebp-2C]106134E2 |. 50 push eax ; /Arg9106134E3 |. 8D4D E0 lea ecx,dword ptr ss:[ebp-20] ; |106134E6 |. 51 push ecx ; |Arg8106134E7 |. 8D55 F8 lea edx,dword ptr ss:[ebp-8] ; |106134EA |. 52 push edx ; |Arg7106134EB |. 8D45 CC lea eax,dword ptr ss:[ebp-34] ; |106134EE |. 50 push eax ; |Arg6106134EF |. 8D4D F4 lea ecx,dword ptr ss:[ebp-C] ; |106134F2 |. 51 push ecx ; |Arg5106134F3 |. 8D55 E8 lea edx,dword ptr ss:[ebp-18] ; |106134F6 |. 52 push edx ; |Arg4106134F7 |. 8D45 D8 lea eax,dword ptr ss:[ebp-28] ; |106134FA |. 50 push eax ; |Arg3106134FB |. 8D4D D0 lea ecx,dword ptr ss:[ebp-30] ; |106134FE |. 51 push ecx ; |Arg2106134FF |. 56 push esi ; |Arg110613500 |. E8 EBEBFFFF call PBSYS125.106120F0 ; \PBSYS125.106120F010613505 |. 8B46 4C mov eax,dword ptr ds:[esi+4C]10613508 |. 83C4 24 add esp,241061350B |. F6C4 08 test ah,81061350E |. 75 03 jnz short PBSYS125.106
13513106135
10 |. 8B5D 14 mov ebx,dword ptr ss:[ebp+14]10613513 |> 56 push esi10613514 |. E8 870B0000 call PBSYS125.106140A010613519 |. 6A 01 push 11061351B |. E8 72130700 call <jmp.&PBSHR125.#1145>10613520 |. 83C4 08 add esp,810613523 |. 8BF8 mov edi,eax10613525 |. E8 E0130700 call <jmp.&PBSHR125.#1105>1061352A |. 8BCE mov ecx,esi1061352C |. 8946 4C mov dword ptr ds:[esi+4C],eax1061352F |. E8 BCE1FFFF call PBSYS125.106116F010613534 |. 85C0 test eax,eax10613536 |. 8945 08 mov dword ptr ss:[ebp+8],eax10613539 |. 0F84 ED010000 je PBSYS125.1061372C1061353F |. F646 4C 01 test byte ptr ds:[esi+4C],110613543 |. 74 0C je short PBSYS125.106
13551106135
45 |. 8B56 04 mov edx,dword ptr ds:[esi+4]10613548 |. 52 push edx ; /Arg110613549 |. E8 32BE0600 call PBSYS125.1067F380 ; \PBSYS125.1067F3801061354E |. 83C4 04 add esp,410613551 |> 53 push ebx ; /Arg110613552 |. E8 09D9FFFF call PBSYS125.10610E60 ; \PBSYS125.10610E6010613557 |. 83C4 04 add esp,41061355A |. 85C0 test eax,eax1061355C |. 8945 08 mov dword ptr ss:[ebp+8],eax1061355F |. 0F84 C7010000 je PBSYS125.1061372C10613565 |. 56 push esi ; /Arg110613566 |. E8 55DDFFFF call PBSYS125.106112C0 ; \PBSYS125.106112C01061356B |. 83C4 04 add esp,41061356E |. 85C0 test eax,eax10613570 |. 8945 08 mov dword ptr ss:[ebp+8],eax10613573 |. 0F84 B3010000 je PBSYS125.1061372C10613579 |. F646 4C 01 test byte ptr ds:[esi+4C],11061357D |. 74 22 je short PBSYS125.106135A11061357F |. 6A 01 push 1 ; /Arg4 = 0000000110613581 |. 68 40B36910 push PBSYS125.1069B340 ; |Arg3 = 1069B34010613586 |. 68 54B36910 push PBSYS125.1069B354 ; |Arg2 = 1069B3541061358B |. 56 push esi ; |Arg11061358C |. E8 0F5C0100 call PBSYS125.PB_UtilGetProfInt ; \PB_UtilGetProfInt10613591 |. 85C0 test eax,eax10613593 |. 74 0C je short PBSYS125.106135A110613595 |. 8B46 04 mov eax,dword ptr ds:[esi+4]10613598 |. 50 push eax10613599 |. E8 D2FB0400 call PBSYS125.106631701061359E |. 83C4 04 add esp,4106135A1 |> 8B46 4C mov eax,dword ptr ds:[esi+4C]106135A4 |. B3 31 mov bl,31106135A6 |. 84C3 test bl,al106135A8 |. 74 40 je short PBSYS125.106135EA106135AA |. 84C0 test al,al106135AC |. 78 3C js short PBSYS125.106135EA106135AE |. F6C4 08 test ah,8106135B1 |. 75 37 jnz short PBSYS125.106135EA106135B3 |. 56 push esi106135B4 |. E8 577A0500 call PBSYS125.1066B010106135B9 |. 8B56 04 mov edx,dword ptr ds:[esi+4] ; |106135BC |. 8D4D FC lea ecx,dword ptr ss:[ebp-4] ; |106135BF |. 51 push ecx ; |Arg2106135C0 |. 52 push edx ; |Arg1106135C1 |. E8 5AAC0500 call PBSYS125.1066E220 ; \PBSYS125.1066E220106135C6 |. 8B45 FC mov eax,dword ptr ss:[ebp-4]106135C9 |. 83C4 0C add esp,0C106135CC |. 85C0 test eax,eax106135CE |. 74 1A je short PBSYS125.106135EA106135D0 |. 8B4D D4 mov ecx,dword ptr ss:[ebp-2C]106135D3 |. 85C9 test ecx,ecx106135D5 |. 74 0D je short PBSYS125.106135E4106135D7 |. 8B55 D4 mov edx,dword ptr ss:[ebp-2C]106135DA |. 8B08 mov ecx,dword ptr ds:[eax]106135DC |. 52 push edx106135DD |. 50 push eax106135DE |. FF51 14 call dword ptr ds:[ecx+14]106135E1 |. 8B45 FC mov eax,dword ptr ss:[ebp-4]106135E4 |> 8B10 mov edx,dword ptr ds:[eax]106135E6 |. 50 push eax106135E7 |. FF52 08 call dword ptr ds:[edx+8]106135EA |> 8D45 FC lea eax,dword ptr ss:[ebp-4]106135ED |. 50 push eax106135EE |. E8 09120700 call <jmp.&PBSHR125.#1101>106135F3 |. 83C4 04 add esp,4106135F6 |. 85C0 test eax,eax106135F8 |. 7C 1C jl short PBSYS125.106
13616106135
FA |. 837D FC 14 cmp dword ptr ss:[ebp-4],14106135FE |. 7D 16 jge short PBSYS125.10613616 ; 判断是不是用了10天 开始对话框 提醒了吧10613600 |. 8B4E 28 mov ecx,dword ptr ds:[esi+28] ; 我目前还剩9天了 肯定是 不跳 执行这里了10613603 |. 51 push ecx ; /Arg210613604 |. 56 push esi ; |Arg110613605 |. E8 468CFFFF call PBSYS125.1060C250 ; \PBSYS125.1060C2501061360A |. 8B45 FC mov eax,dword ptr ss:[ebp-4]1061360D |. 83C4 08 add esp,810613610 |. 85C0 test eax,eax10613612 |. 7F 0B jg short PBSYS125.1061361F10613614 |. EB 07 jmp short PBSYS125.1061361D
2016年01月17日 01点01分
2